
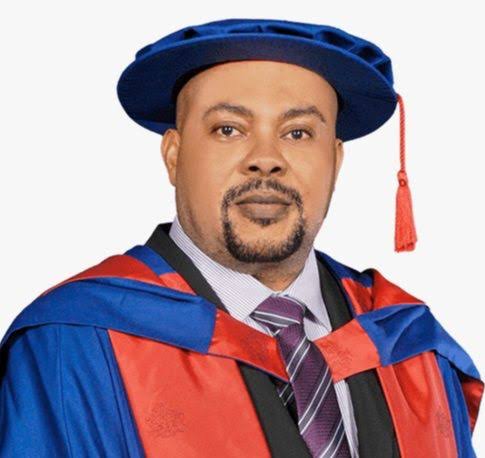
A leading information security expert, Dr Kingsley Chibuzor Aguoru, has raised alarm over the continued use of SMS-based One-Time Passcodes, insisting the method is outdated and should be urgently replaced.
Widely regarded as one of the earliest innovators behind SMS-delivered OTPs, Aguoru said the technology no longer offers the level of protection required in today’s digital threat landscape.
Recounting the origins of his work, the cybersecurity specialist explained that his interest in payment security took shape after he became a victim of triangulation fraud in the early 2000s.
According to him, that experience pushed him to design one of the world’s first SMS OTP delivery systems for card authentication, called Smsverify, in 2005 while studying at the University of Liverpool.
In his words, the concept introduced an additional verification layer aimed at securing online card transactions and banking access. Although major global payment networks initially dismissed the idea, he said it later gained acceptance.
Early adoption of the system, he noted, came from Paymenex, a UK-based alternative payment operator serving developing economies where online fraud risks were already emerging.
Over the years, SMS OTPs evolved into a global benchmark for two-factor authentication across banking, fintech and digital services worldwide.
However, Aguoru now says the method is no longer reliable, arguing that telecom infrastructure has remained stagnant while cyber threats have grown more sophisticated.
He pointed out that the networks responsible for delivering text messages—particularly the ageing SS7 signalling protocol and SMS Centres—still lack modern encryption and proper authentication mechanisms.
Because attackers can exploit phone networks, compromise SIM cards or manipulate telecom routing systems, he warned that text messages are easily intercepted, redirected or spoofed.
These weaknesses, he added, expose SMS OTP users to threats such as SIM swapping, phishing schemes, RDP-based intrusions and other advanced cyberattacks.
To address these risks, Aguoru urged banks, fintech companies and online service providers to begin transitioning to stronger verification tools.
Among the recommended alternatives are passkeys, authenticator apps, hardware-based tokens and secure push-notification approval systems built on modern cryptographic standards.
Passkeys, he said, should be prioritised because they use public-key cryptography and comply with FIDO Alliance specifications that eliminate reliance on telecom operators.
While acknowledging that SMS OTP played a crucial role when digital banking was still emerging—especially in developing countries—Aguoru maintained that the technology has outlived its usefulness.
He concluded that rising cybercrime demands stronger systems, saying: “What worked in 2005 cannot be the foundation of digital security in 2025.”
